Imprivata ID

Screenshots
Details
- Rating
- 234.00 reviews
- Version
- 2026.1.1.144
- Developer
- Imprivata, Inc
Analysis by Norviv
In a hospital or clinic, authentication is not a small inconvenience. A clinician may need to open a workstation, review a patient record, or move between shared computers while keeping access tied to the right person. Imprivata ID is a free medical app from Imprivata, Inc. that is designed for that kind of professional environment. I see it less as a general-purpose authenticator and more as one part of a controlled clinical sign-in process.
That distinction matters. If you are looking for a personal security app for email, banking, or social accounts, this is probably not the natural choice. Its purpose is narrower: to support secure authentication and smoother clinical workflows for medical professionals. The app is available to everyone by age rating, but practical usefulness depends heavily on whether your workplace uses the Imprivata system and has configured access for you.
My overall impression is cautious but positive. The idea is sensible, especially where staff need to authenticate without turning every workstation change into a long interruption. At the same time, an authentication app cannot be judged only by how quickly it opens or how polished its screens look. The important questions are whether it fits the organization’s setup, what choices the user sees during sign-in, and how it behaves when a phone, account, or connection is unavailable.
Where Imprivata ID fits in a clinical workflow
Imprivata ID belongs to the medical category, and its role is closely connected to workplace identity rather than independent consumer use. In my view, that is its strongest point and also its biggest limitation. A hospital employee who has already been instructed to use Imprivata may find the app useful because it is aligned with the organization’s authentication process. Someone downloading it casually will not get the same value simply by installing it.
A realistic scenario would be a nurse moving between several treatment areas during a shift. Instead of treating each workstation as a completely separate login problem, the employee may use the organization’s approved authentication flow to confirm identity and continue working. The benefit is not just speed. In a clinical setting, reducing unnecessary sign-in friction can help staff spend more attention on patients while still keeping access controlled.
That does not mean the app replaces every other identity check. The exact experience depends on the employer’s configuration, the systems connected to it, and the authentication methods made available to the user. I would not install it expecting it to unlock unrelated medical portals or act as a universal replacement for a standard authenticator. Its value is tied to the environment around it.
The app has been available since May 27, 2016, and its current version is 2026.1.1.144. It supports Android 6.0 and later, which gives it a broad compatibility range on Android devices. Still, compatibility with the phone is only one part of the decision. Before relying on it for work, I would confirm that the organization supports the device, the account has been enrolled, and the relevant clinical systems recognize the authentication flow.
Stories Picked for You

Life360 Works Better When Your Household Agrees on What to Share

YouVersion Bible Fits Scripture into Everyday Phone Routines

Matchington Mansion Review: Match-Three Puzzles With a Place to Restore

Android Auto Shows Why Safer Driving Software Does Less

Google Find Hub Runs on Shared Devices and Quiet Trust

Sygic GPS Navigation: The Ultimate Offline Travel Companion
Imprivata ID is free to download, which removes one obvious barrier for staff and organizations evaluating it. That should not be confused with independent access to a service. In practice, an authentication tool can be free at the app level while still requiring an employer-managed account, enrollment, or administrative setup. I would check those requirements before spending time troubleshooting an installation that was never activated for the workplace.
Trust begins with the surrounding account
When I assess an app that handles authentication, I pay attention to the boundary between the app and the organization controlling access. Imprivata ID is intended for professional use, so the trust decision is not only about the developer, Imprivata, Inc. It also involves the employer’s identity policies, device rules, recovery process, and support desk. A well-managed account can make the experience dependable; a poorly explained enrollment process can make even a sound tool feel confusing.
The public reception is mixed rather than flawless. The app has an average rating of 3.0 from around 509 ratings, with around 234 written reviews. I would not treat that score as a direct measurement of authentication quality because workplace configuration, device restrictions, and account problems can all affect a review. Still, it is a useful reminder that this is not an app I would recommend blindly. Users should know who supports it when something goes wrong.
One practical question is what happens when a phone is replaced. For a regular consumer app, reinstalling and signing in may be enough. For a workplace authentication tool, the organization may need to verify the user or re-enroll the device. I would not assume that restoring a phone backup automatically restores access. Before changing devices, I would ask the employer’s support team about the approved transfer or recovery procedure.
The same caution applies to a lost phone. The sensible response is not simply to delete the app and hope access disappears. The account or device may need to be disabled through the organization’s administrative process. If you use Imprivata ID for work, save the support contact and emergency procedure somewhere separate from the phone. That small preparation can matter more than any individual setting inside the app.
What I would check before depending on it
My first check would be enrollment. I would confirm that the app is being issued or approved by the employer, that the correct work account is being used, and that the expected sign-in prompt appears. If the app opens but does not connect to the workplace workflow, that does not necessarily mean the phone is defective. It may simply be waiting for an administrator-side setup step.
My second check would be the visible choices during authentication. I would look for clear prompts, understandable error messages, and an obvious way to cancel or retry. Authentication should not encourage hurried guesses, especially when a clinician is working under pressure. If a prompt appears unexpectedly, I would pause rather than approve it automatically. That habit is useful with any authentication system.
My third check would be recovery. I would ask how to proceed if the phone is offline, the battery is empty, the device is unavailable, or the account is locked. The right backup may be an organization-managed alternative rather than something the user can configure alone. Knowing that before a shift begins is a concrete advantage, because a sign-in problem in the middle of patient care is much harder to solve calmly.
I would also review the app’s permissions and privacy information directly on the device and in the organization’s documentation. I do not assume that an authentication app has access to clinical records simply because it is used near them, nor do I assume the opposite without checking. Trust should come from visible permissions, clear account controls, and an understandable support path—not from the app’s category alone.
Data-sensitive moments deserve extra care
The most sensitive moment is not necessarily the initial installation. It is the point at which the app is paired with a professional identity and used to approve access. I would pay attention to the account being enrolled, the device being registered, and any confirmation that links the phone to workplace credentials. If the wrong account is selected, the problem may be more serious than an ordinary app login mistake.
I would avoid enrolling a shared or borrowed phone unless the organization explicitly permits it. A personal device can be convenient, but it creates a clear separation question: who controls the phone, who can unlock it, and what happens when the employee leaves the organization? Those are not abstract privacy concerns. They affect whether authentication remains under the right person’s control.
Notifications deserve the same attention. I would check whether authentication prompts reveal more information than necessary on a locked screen and adjust the phone’s notification visibility if appropriate. I am not claiming that every installation exposes sensitive content; the point is to inspect what is actually displayed on your device. A prompt that is harmless in a private setting may be less suitable on a phone visible to colleagues or members of the public.
Another data-sensitive situation is troubleshooting. When support asks for screenshots or diagnostic details, I would remove patient information and unrelated account details before sharing anything. An authentication problem should not lead to accidental disclosure of clinical content. The safest workflow is to follow the organization’s approved support channel and provide only what is needed to identify the problem.
For the same reason, I would not use screenshots, copied codes, or informal workarounds as a permanent substitute for the official process. They can create records in the phone’s gallery, clipboard, or messages, and they may be visible to other apps or people with access to the device. The more sensitive the workplace, the more important it is to keep authentication actions inside the intended flow.
User control is more than a sign-in button
What I want from Imprivata ID is a clear sense of agency. I should know which account I am approving, what action is being requested, and whether I can decline or retry without getting trapped. If an approval arrives when I did not initiate a sign-in, I would reject it and report the event through the workplace process rather than treating it as a harmless glitch.
Account control also includes knowing when access ends. If you change roles, leave an employer, or stop using a managed device, ask how the account and device registration are removed. Deleting the application may clean up the phone, but it may not be the complete organizational offboarding step. I consider that an important difference between a workplace authentication app and a casual utility.
The broad age rating of Everyone makes the app approachable from a store perspective, but it should not be read as a sign that the app is intended for children or general household use. The meaningful audience is medical professionals and other staff whose organizations have adopted the relevant authentication workflow. That is why I would judge it by workplace clarity and recovery options rather than by entertainment-style polish.
It is also worth separating user control from administrative control. An employee may be able to approve or reject a sign-in, but the organization may control enrollment, supported devices, session behavior, and account recovery. That arrangement can be appropriate for clinical security, yet it means the user should know which problems can be solved locally and which require an administrator.
For day-to-day use, I would keep the phone updated, protect the device with its own lock, and avoid disabling security features just to make authentication faster. I would also test the workflow before a busy shift, especially after an operating-system update, phone replacement, or change in workplace credentials. These steps are not glamorous, but they reduce the chance of discovering a setup problem when quick access matters.
How it compares with familiar alternatives
Compared with a general authenticator app, Imprivata ID is more specialized. A standard authenticator is often useful across many unrelated online accounts and may give an individual more direct control over adding or removing services. Imprivata ID makes more sense when the employer has built its clinical access process around Imprivata. Choosing between them is therefore less about which interface looks better and more about which system your organization actually supports.
Compared with passwords alone, a dedicated authentication step can reduce dependence on repeatedly typing credentials at shared workstations. That can be helpful in a busy clinical environment. The trade-off is that the phone becomes part of the access chain. If the phone is unavailable, the organization needs a practical fallback, and the user needs to understand it before an urgent situation occurs.
Compared with hardware security keys, a phone-based method may be easier for staff who already carry a device, while a physical key can be simpler to separate from personal data and phone notifications. I would not call one universally better. The appropriate option depends on the organization’s security policy, the clinical setting, and how reliably staff can keep the required device available.
Compared with a workplace single sign-on system that operates without a separate phone interaction, Imprivata ID may add a step but can provide a visible confirmation point. Whether that feels like an improvement depends on the workflow design. If prompts are clear and the process is quick, the extra confirmation may be reassuring. If enrollment and recovery are poorly explained, the same step can become a source of delays.
Who should use it, and who should look elsewhere
I would recommend considering Imprivata ID if you are a medical professional whose employer specifically uses Imprivata for authentication. It is also a reasonable fit for organizations trying to make access across clinical workstations more consistent without relying entirely on passwords. The large installation base—over 500 thousand installs—suggests that it is used beyond a tiny pilot audience, although popularity alone does not guarantee a smooth experience at every workplace.
I would skip it if you want a personal authenticator for unrelated accounts, if your employer has not instructed you to use it, or if you need an app that works independently of organizational enrollment. Installing it in those situations is unlikely to solve a real problem. I would also hesitate if your workplace cannot explain device replacement, lost-phone response, or account recovery. Those operational answers are essential for an authentication tool.
For a small clinic without an Imprivata deployment, a different authenticator selected by its own security administrator may be more practical. For a person managing personal accounts, a well-supported general authenticator may offer broader flexibility. For a highly controlled environment that forbids personal phones, a hardware-based or workstation-integrated method could be a better match. The right choice is the one that fits the access policy rather than the one with the broadest store appeal.
My cautious verdict after weighing the trade-offs
Imprivata ID has a clear professional purpose, and I appreciate that it is aimed at a real clinical friction point: confirming identity while staff move through demanding workflows. Its free price and support for Android 6.0 and later make initial access straightforward on compatible devices. The developer, Imprivata, Inc., also gives the app a clear identity instead of presenting it as an anonymous utility.
My reservation is that the app cannot be evaluated in isolation. The quality of the experience depends on enrollment, workplace configuration, visible prompts, device ownership, and the support process around a lost or replaced phone. The average rating of 3.0 is not a reason to dismiss it, but it is enough to encourage careful testing rather than assuming that every installation will be effortless.
If I were advising a colleague, I would say this: install it only through the organization’s approved process, verify the account before approving anything, inspect the phone’s notification and permission behavior, and learn the recovery route before you need it. Those habits give the user more control and reduce the risk of turning a convenient authentication step into a workplace obstacle.
My final view is that Imprivata ID is a sensible specialist tool for institutions already using the Imprivata ecosystem, but a poor choice as a general-purpose authenticator. For the right clinical environment, it can support a smoother sign-in routine. For everyone else, the lack of independent usefulness is a decisive limitation. I would recommend it conditionally, with trust based on the organization’s controls and the user’s ability to understand and manage the authentication process.
Frequently Asked Questions
01What is Imprivata ID used for?
Imprivata ID is a mobile authentication app designed to help users securely verify their identity when accessing supported business systems, applications, or remote resources. It commonly works as part of an organization’s multi-factor authentication setup, adding an extra security step beyond a username and password. The app is mainly intended for employees, contractors, and other authorized users whose organization has enabled Imprivata authentication services.
02How does Imprivata ID authentication work?
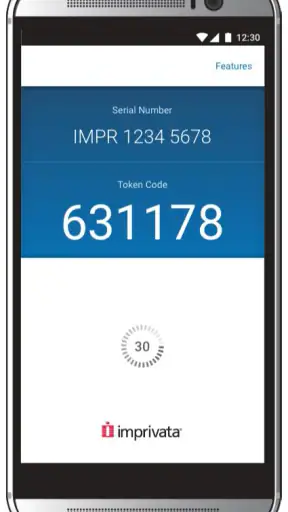
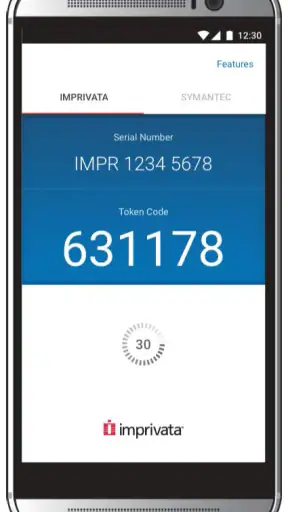
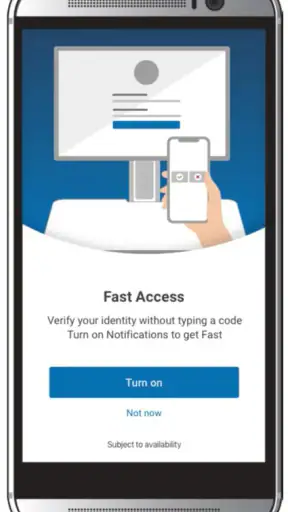
After your organization enrolls your device, Imprivata ID can receive authentication requests or generate security codes, depending on the configuration used by your employer or service provider. You may need to approve a sign-in request within the app, enter a one-time passcode, or use an available device security method. The exact process varies, so installation alone does not provide access without administrator setup.
03Is Imprivata ID safe to use on Android or iPhone?
Imprivata ID is built for secure authentication and is intended to protect access to organizational accounts and systems. Its security depends on factors such as device protection, application permissions, network conditions, and your organization’s configuration. Users should keep the app and operating system updated, use a screen lock or biometric protection, and never share authentication codes or approve sign-in requests they did not initiate.
04Does Imprivata ID work without an internet connection?
Whether Imprivata ID works offline depends on the authentication method configured by your organization. Some setups may allow the app to generate a time-based passcode without an active connection, while push notifications and certain enrollment or verification steps generally require internet access. If you are traveling or working in an area with unreliable connectivity, ask your IT administrator whether offline authentication is supported for your account.
05What should I do if I lose my phone or cannot access Imprivata ID?
If your phone is lost, replaced, reset, or unavailable, contact your organization’s IT or help desk as soon as possible so they can protect your account and help you enroll another device. Avoid repeatedly attempting sign-ins if the app is not responding, and do not install unofficial versions or share recovery information with others. Administrators may need to revoke the old device and issue a new enrollment process.


